Penetration Testing

Find and Fix Vulnerabilities Before Attackers Do

We follow OWASP methodology to simulate real-world attacks against your web applications, APIs and AWS environment — then hand you clear, prioritized fixes.

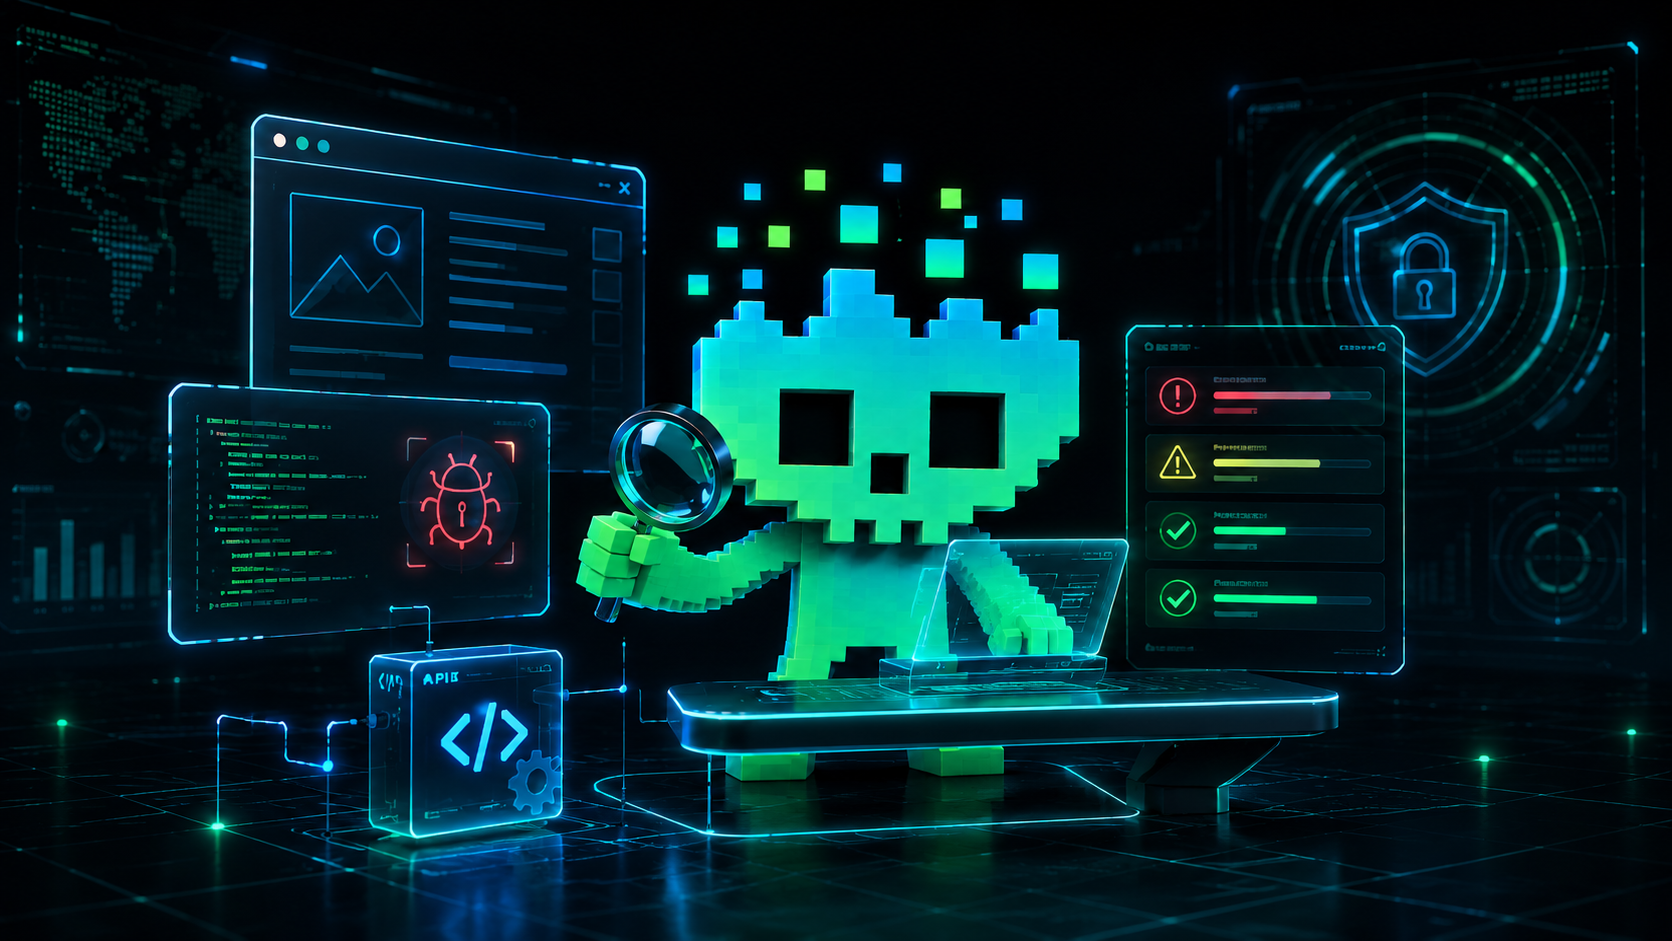
Huma Hack mascot performing penetration testing — inspecting code, APIs and web apps for vulnerabilities
Key Benefits

Testing That Reflects Reality

Real-World Testing

Realistic automated and manual attacks that mirror how adversaries actually target your systems.
Unlimited Retesting (30 days)

Fix the findings and we'll re-test them — as many times as needed within 30 days — to confirm they're truly closed.

Compliance Ready

Reports built to satisfy ISO 27001, SOC 2 and customer/vendor security reviews.

What We Test

Focused Where It Matters

Web Application Testing

OWASP Top 10 and beyond — authentication, access control, injection, business-logic flaws and more.

API Security Testing

REST and GraphQL APIs — broken object-level authorization, excessive data exposure, rate limiting and abuse cases.

Cloud Pentesting

AWS misconfigurations, excessive permissions, exposed assets and privilege-escalation paths.
Our Approach

Exploit, Document, Explain

  • Realistic automated and manual attacks — not just a scanner run.
  • We exploit, document and explain every finding so your team understands the real risk.
  • Clear, prioritized reports with technical findings and executive summaries.
  • Remediation support and fix validation so issues get closed, not just listed.
Huma Hack offensive security mascot
FAQ

Penetration Testing Questions

We focus on what we do exceptionally well: web applications, APIs (REST and GraphQL) and AWS cloud environments. We don't offer network, mobile or on-prem hardware testing today — and we'll tell you honestly if your need falls outside our scope.
Both. Automated tooling gives us coverage; skilled manual testing finds the business-logic and chained vulnerabilities scanners miss.
Yes — unlimited retesting for 30 days after the engagement, so you can confirm your fixes actually resolve each finding.
Yes. Our reports are structured for ISO 27001 and SOC 2 evidence and for vendor/customer security questionnaires, with both technical detail and an executive summary.
We agree scope, timing and rules of engagement up front and test carefully to avoid impact. Where appropriate we test against staging environments that mirror production.
Get Started

Ready to Test Your Web, API, or AWS Environment?