ISO 27001 Certification

Get ISO 27001 Certified — Globally Recognized

A turnkey path to an internationally valid ISO 27001 certificate, issued by an IAF-accredited registrar. No complicated platforms. No endless consulting hours. Just results — in around three weeks on average.

Huma Hack mascot presenting an ISO 27001 Information Security Management System certificate
Key Benefits

Why Certify with Huma Hack

Save Time

A managed, streamlined process gets you to certification fast — on average in about three weeks — without derailing your team.
Save Money

No expensive platforms or open-ended consulting retainers. One clear scope, one predictable investment.

Global Certification

Your certificate is issued by an accredited body on the IAF platform — recognized and trusted worldwide.
What You Receive

Everything You Need to Get — and Stay — Certified

  • A complete, customized ISMS package — 62 documents tailored to your organization.
  • A certificate issued by an accredited certification body registered on the IAF platform.
  • Huma Hack representation through your Stage 1 & Stage 2 audits — at no additional cost.
  • Post-certification guidance: management reviews, internal audits and supplier management.
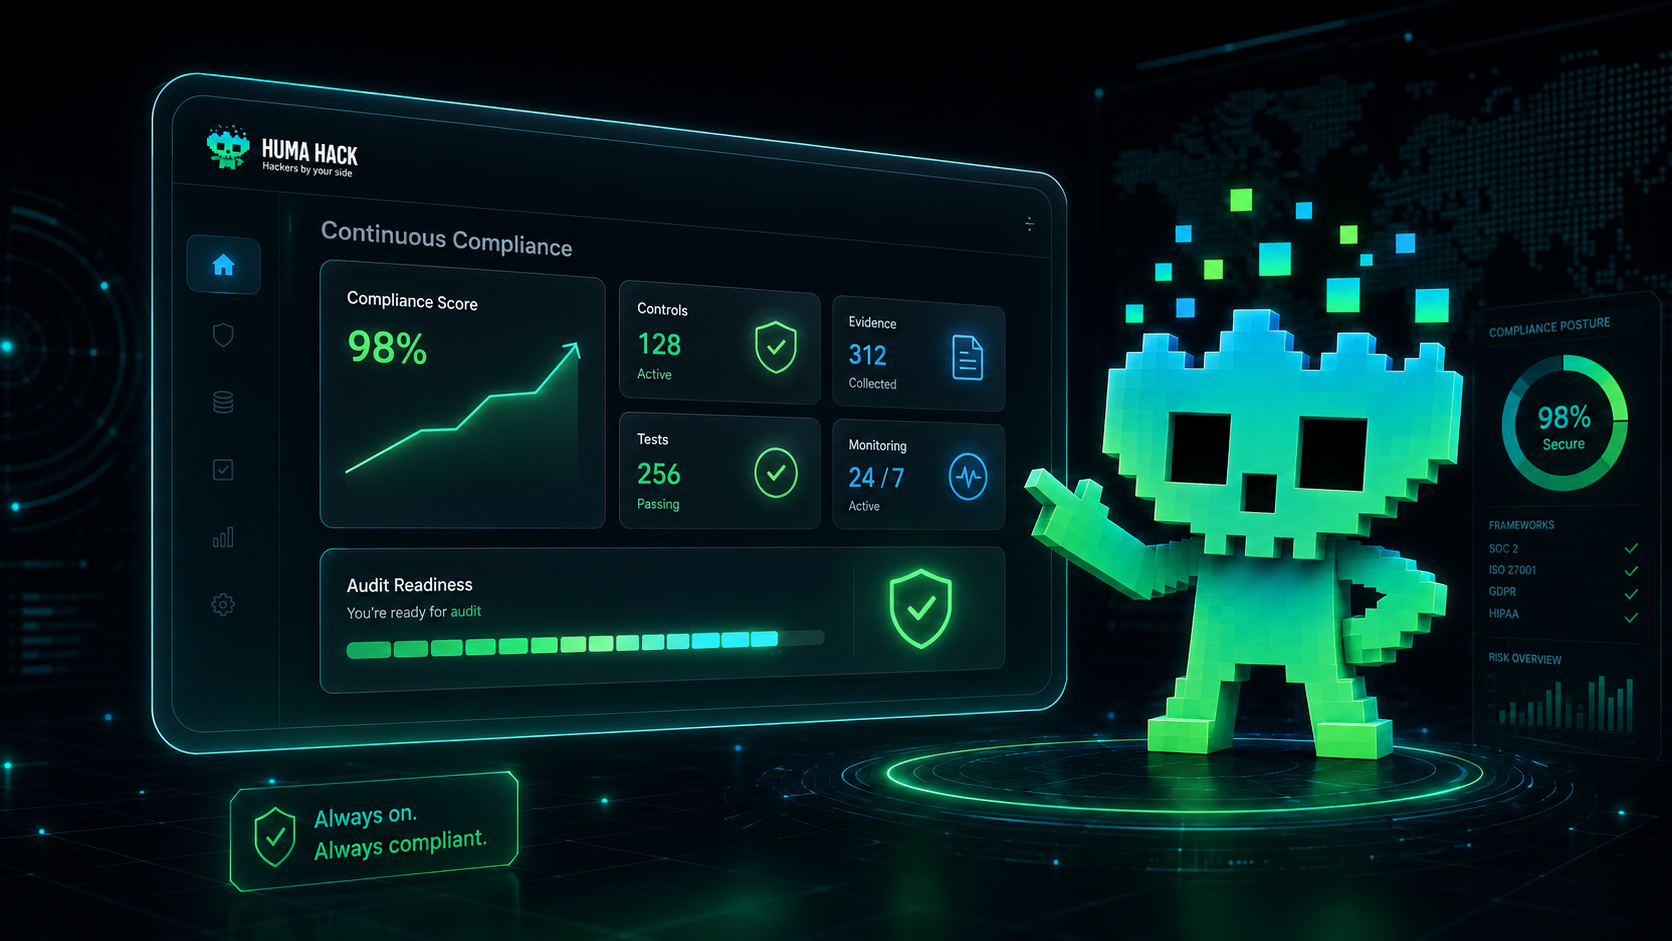
ISO 27001 ISMS and continuous compliance dashboard showing 98% compliance and audit readiness
The Path to Certification

Four Phases to Your Certificate

Preparation

A GAP analysis maps where you are today against the ISO 27001 requirements.

Planning & Design

We define scope, risk methodology and the policies that fit how you actually work.

Implementation

We build the 62-document ISMS, the risk register and your Statement of Applicability (SoA).

Evaluation & Certification

Internal audit, then Stage 1 and Stage 2 with the registrar — ending in your certificate.
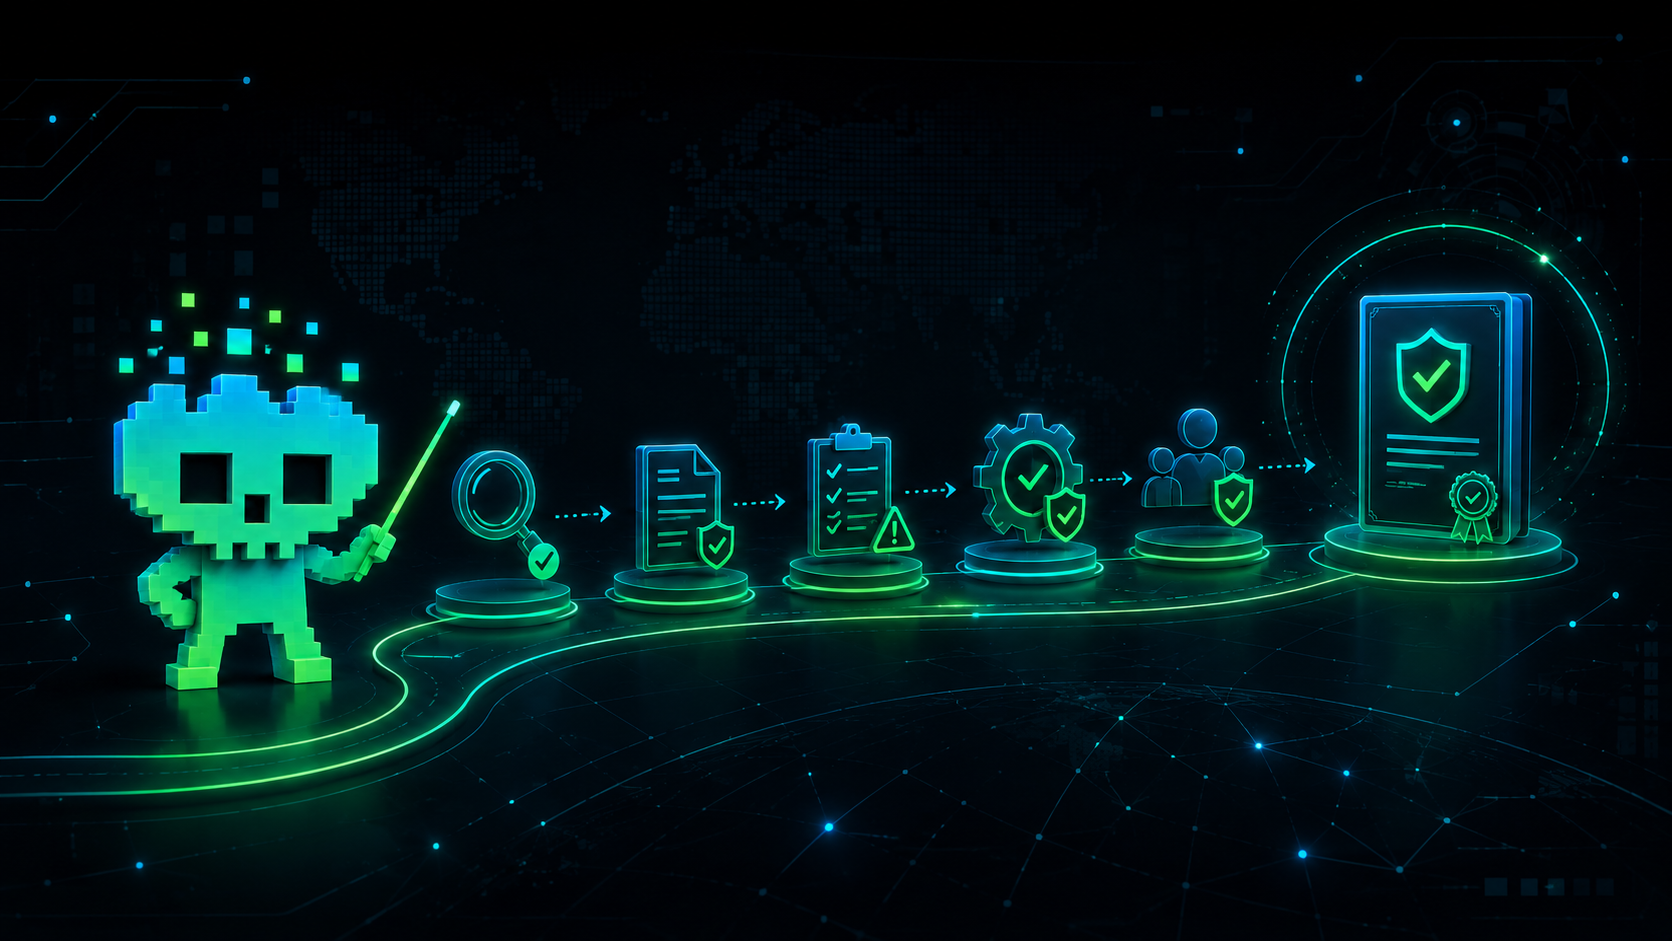
Huma Hack ISO 27001 certification path: GAP analysis, documentation, checklist, implementation, audit and final certificate
Huma Hack mascot celebrating certification
After Certification

A Long-Term Compliance Partner

ISO 27001 runs on a three-year cycle: surveillance audits at months 12 and 24, and re-certification at month 36. Huma Hack accompanies every audit.

As you grow — new staff, new cloud regions, or expansion into SOC 2, GDPR or NIS2 — we keep your ISMS current and audit-ready, so compliance never becomes a fire drill.

Vanta Partner

Continuous Compliance, Powered by Vanta

As a Vanta Partner, we can automate the ongoing work of compliance: continuous evidence collection, risk management aligned to ISO 27005, automated access reviews, vendor risk tracking, and a public Trust Center that shows customers you take security seriously.
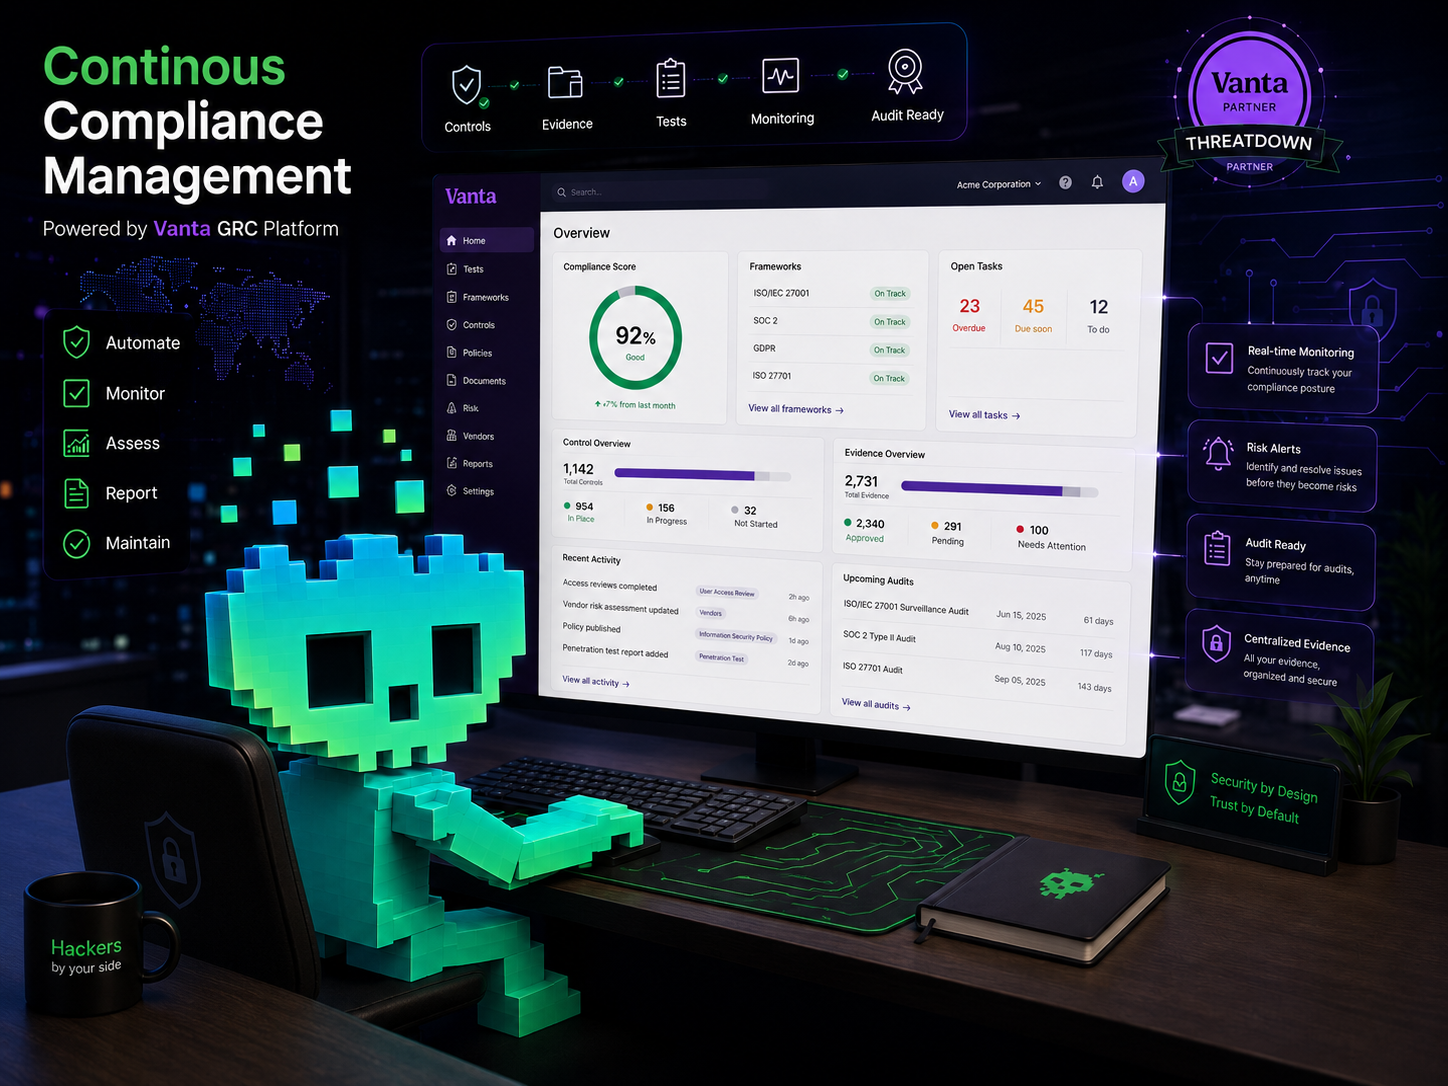
Continuous Compliance Management powered by the Vanta GRC platform — Huma Hack, Vanta and ThreatDown Partner
FAQ

ISO 27001 Questions

Yes. Your certificate is issued by an accredited certification body registered on the IAF platform, making it valid and trusted worldwide.
On average, around three weeks to reach certification — depending on your scope and how quickly your team can review and approve.
No complicated platforms and no endless consulting hours are required. We build the ISMS for you, and can add continuous-compliance automation with Vanta where it adds value.
Yes. Huma Hack represents you through both the Stage 1 and Stage 2 audits at no additional cost.
ISO 27001 runs on a three-year cycle with surveillance audits at months 12 and 24 and re-certification at month 36. We accompany every audit and keep your ISMS current as you grow.
Get Started

Let's Get You ISO 27001 Certified Now!